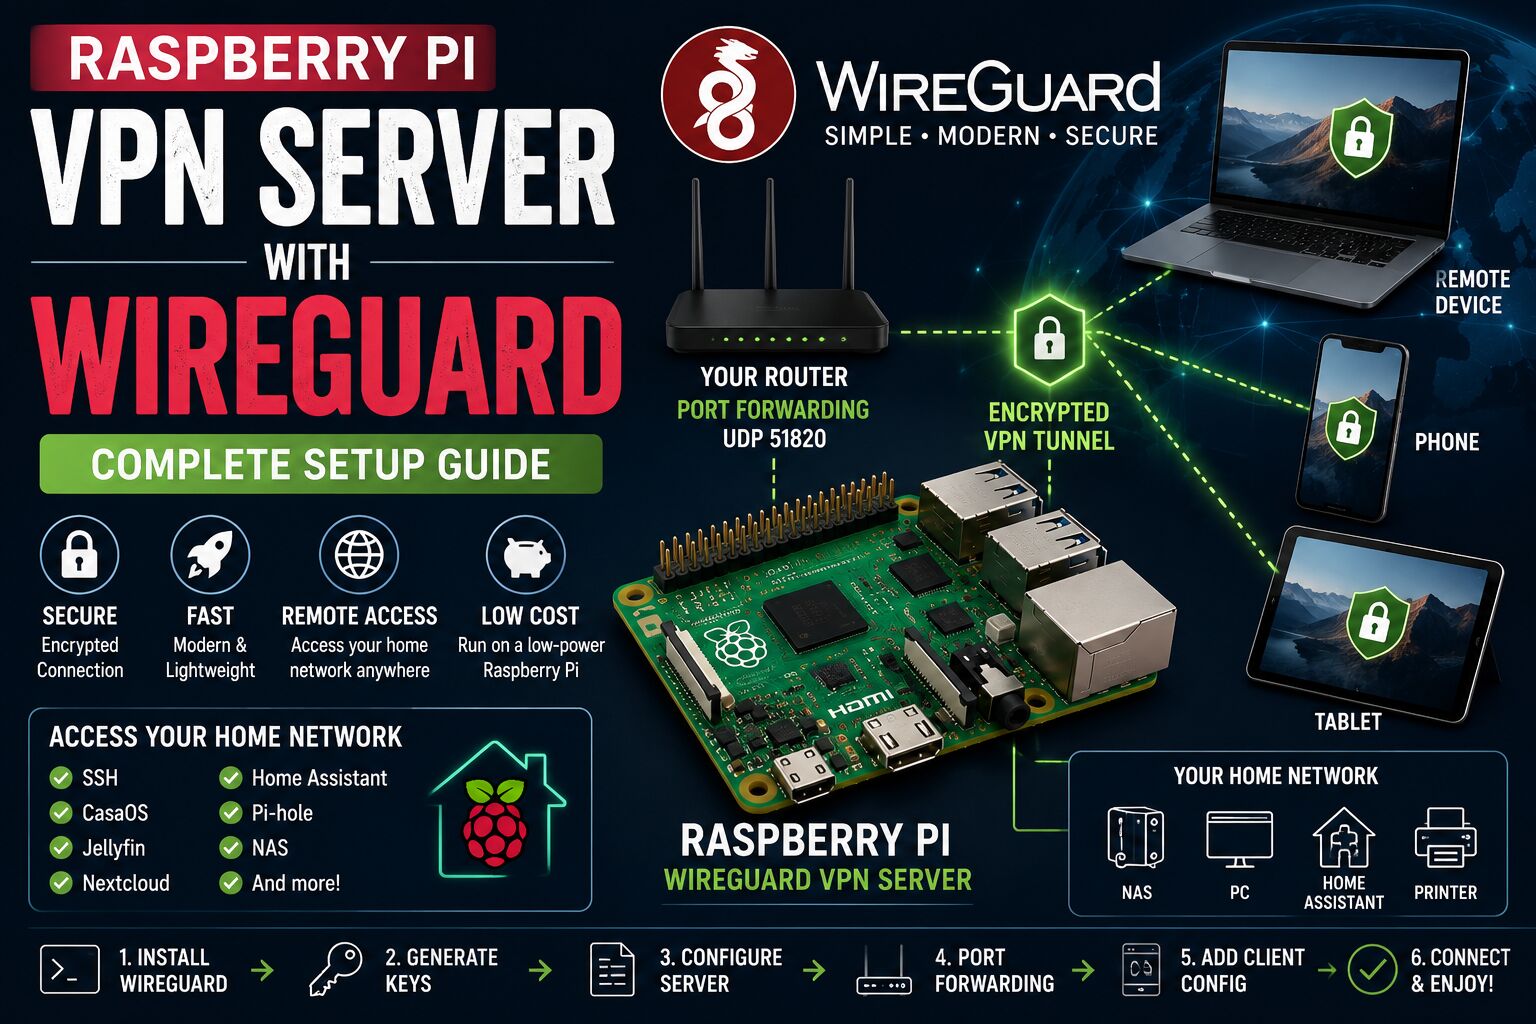
A Raspberry Pi can be turned into a powerful VPN server that lets you securely connect to your home network when you’re away.
With WireGuard, you can access your Raspberry Pi, NAS, Home Assistant, Jellyfin, Nextcloud, printers, and other devices as if you were connected to your home network.
WireGuard is designed as a modern VPN protocol with a relatively simple configuration. On Raspberry Pi OS, WireGuard can be installed directly through the standard package system. (WireGuard)
In this guide, we’ll build a WireGuard VPN server from scratch on a Raspberry Pi.
Important: This guide assumes that your Internet connection allows incoming connections. If your ISP uses CGNAT, traditional port forwarding may not work. In that situation, a solution such as Tailscale or a VPN server hosted on a VPS may be a better option.
What Is WireGuard?
WireGuard is a modern VPN protocol that creates an encrypted tunnel between devices.
Instead of exposing individual services on your home network, you can connect to your VPN first:
                    Internet
                       │
                       │ Encrypted VPN
                       ▼
                  ┌──────────┐
                  │ Router   │
                  └────┬─────┘
                       │
                 UDP 51820
                       │
                 ┌─────▼─────┐
                 │ Raspberry │
                 │    Pi     │
                 │ WireGuard │
                 └─────┬─────┘
                       │
                 Home Network
              ┌────────┼────────┐
              │        │        │
             NAS    Home Assistant  PC
Once connected, your remote device can access resources on your home network according to the routing configuration you choose.
Why Use a Raspberry Pi as a VPN Server?
A Raspberry Pi is well suited to this role because it can run continuously while consuming relatively little power.
Advantages
- Low power consumption
- Small footprint
- Affordable
- Always-on operation
- Ethernet connectivity
- Linux support
- WireGuard support
- Can run other home-server applications
A Raspberry Pi 4 or Raspberry Pi 5 is more than capable of handling a typical personal VPN deployment.
What Can You Access Through the VPN?
Once connected, you could access services such as:
- SSH
- CasaOS
- Jellyfin
- Nextcloud
- Home Assistant
- Pi-hole
- NAS
- Network printers
- Windows file shares
- Internal websites
- Development servers
- Other LAN devices
For example:
Laptop
   │
   │ WireGuard
   ▼
Raspberry Pi
   │
   ├── CasaOS
   ├── Jellyfin
   ├── Nextcloud
   ├── Pi-hole
   └── Home LAN
This makes WireGuard an excellent addition to a Raspberry Pi home server.
Requirements
You’ll need:
| Component | Recommendation |
|---|---|
| Raspberry Pi | Raspberry Pi 4 or 5 |
| OS | Raspberry Pi OS 64-bit |
| Network | Ethernet recommended |
| Router | Port forwarding capability |
| Public IP | Public IPv4 or suitable IPv6 setup |
| VPN | WireGuard |
| Client | Windows, macOS, Linux, Android, or iOS |
You’ll also need administrative access to your router.
Before Installing WireGuard
There are two important things to check.
1. Does your ISP use CGNAT?
Your router needs to be reachable from the Internet for a traditional self-hosted VPN server.
Some ISPs place customers behind Carrier-Grade NAT (CGNAT).
If you’re behind CGNAT, configuring port forwarding on your router may not be enough because your router doesn’t have a directly reachable public IPv4 address.
A quick way to investigate is to compare:
- Your router’s WAN IPv4 address
- The public IPv4 address shown by an external IP-checking service
If they don’t match, CGNAT is one possible explanation.
Other possibilities include multiple routers or upstream NAT.
If your ISP uses CGNAT, consider:
- Tailscale
- A VPS-based WireGuard setup
- Asking your ISP for a public IPv4 address
Tailscale is particularly convenient because it doesn’t require traditional inbound port forwarding.
2. Give the Raspberry Pi a Stable IP
Your Raspberry Pi should have a stable LAN address.
For example:
Raspberry Pi
192.168.1.50
The easiest approach for many home networks is a DHCP reservation on your router.
This ensures the router always gives the Raspberry Pi the same IP.
Step 1: Update Raspberry Pi OS
Connect to the Raspberry Pi using SSH or a local terminal.
Run:
sudo apt update
sudo apt full-upgrade -y
Then reboot:
sudo rebootReconnect after the Raspberry Pi starts.
Step 2: Install WireGuard
On current Debian-based Raspberry Pi OS installations, WireGuard can be installed from the package repository.
Run:
sudo apt install wireguard wireguard-tools -yWireGuard’s official installation documentation provides package-based installation instructions for Debian and other supported distributions. (WireGuard)
Verify the installation:
wg --versionYou should receive a WireGuard version number.
Step 3: Enable IP Forwarding
The Raspberry Pi needs to route traffic between the WireGuard VPN interface and your normal network interface.
Edit the sysctl configuration:
sudo nano /etc/sysctl.d/99-wireguard.confAdd:
net.ipv4.ip_forward=1If you’re also configuring IPv6 routing, add:
net.ipv6.conf.all.forwarding=1Save the file.
Apply the configuration:
sudo sysctl --systemVerify IPv4 forwarding:
sysctl net.ipv4.ip_forwardYou should see:
net.ipv4.ip_forward = 1IP forwarding is a fundamental part of configuring a Raspberry Pi as a VPN gateway. (Raspberry Pi Forums)
Step 4: Create the WireGuard Directory
WireGuard configuration files are normally stored under:
/etc/wireguard/Create it if necessary:
sudo mkdir -p /etc/wireguardProtect the directory:
sudo chmod 700 /etc/wireguardStep 5: Generate the Server Keys
WireGuard uses public/private key pairs for authentication.
Change into the WireGuard directory:
cd /etc/wireguardSet restrictive permissions:
sudo umask 077Generate the server private key:
sudo wg genkey | sudo tee server_private.keyGenerate the corresponding public key:
sudo cat server_private.key | wg pubkey | sudo tee server_public.keyCheck the files:
sudo ls -l /etc/wireguardYou should have:
server_private.key
server_public.key
Never publish your private key.
The public key can be shared with clients.
Step 6: Generate a Client Key Pair
We’ll create one VPN client for a laptop or phone.
Generate its private key:
sudo wg genkey | sudo tee client1_private.keyGenerate the public key:
sudo cat client1_private.key | wg pubkey | sudo tee client1_public.keyNow you have:
Server:
server_private.key
server_public.key

Client:
client1_private.key
client1_public.key
Step 7: Create the WireGuard Server Configuration
Create:
sudo nano /etc/wireguard/wg0.confUse this as a starting point:
[Interface]
Address = 10.8.0.1/24
ListenPort = 51820
PrivateKey = SERVER_PRIVATE_KEY

PostUp = iptables -A FORWARD -i wg0 -j ACCEPT; iptables -A FORWARD -o wg0 -j ACCEPT; iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE
PostDown = iptables -D FORWARD -i wg0 -j ACCEPT; iptables -D FORWARD -o wg0 -j ACCEPT; iptables -t nat -D POSTROUTING -o eth0 -j MASQUERADE

[Peer]
PublicKey = CLIENT1_PUBLIC_KEY
AllowedIPs = 10.8.0.2/32
Replace:
SERVER_PRIVATE_KEYwith the contents of:
sudo cat /etc/wireguard/server_private.keyAnd replace:
CLIENT1_PUBLIC_KEYwith:
sudo cat /etc/wireguard/client1_public.keyImportant
The example assumes your Raspberry Pi connects to the network through:
eth0Check your interface with:
ip routeYou may see:
default via 192.168.1.1 dev eth0If you’re using Wi-Fi, the interface may instead be:
wlan0Change the PostUp and PostDown rules accordingly.
Understanding the VPN Address Range
The WireGuard VPN will use:
10.8.0.0/24The server will be:
10.8.0.1The first client will be:
10.8.0.2Additional clients could use:
10.8.0.3
10.8.0.4
10.8.0.5
For example:
WireGuard Server
10.8.0.1

Laptop
10.8.0.2

Phone
10.8.0.3

Tablet
10.8.0.4
Step 8: Protect the Configuration File
Because wg0.conf contains your server’s private key, make sure it isn’t readable by ordinary users.
Run:
sudo chmod 600 /etc/wireguard/wg0.confAlso protect the key files:
sudo chmod 600 /etc/wireguard/*.keyStep 9: Configure Your Router
Your router needs to forward the WireGuard UDP port to the Raspberry Pi.
The default port in our example is:
UDP 51820Create a port-forwarding rule:
Protocol: UDP
External Port: 51820
Internal IP: 192.168.1.50
Internal Port: 51820
Replace:
192.168.1.50with your Raspberry Pi’s actual LAN address.
Recent Raspberry Pi documentation also describes WireGuard deployments using UDP port 51820 and router port forwarding. (Raspberry Pi)
Why UDP?
WireGuard uses UDP rather than TCP.
The default WireGuard listening port is:
51820/UDPYou can change the port if necessary, but there usually isn’t a strong reason to do so.
Step 10: Find Your Public IP Address
Your remote VPN client needs to know how to reach your home network.
You could use your public IP:
203.0.113.50But residential Internet connections often have dynamic IP addresses.
A better solution is Dynamic DNS (DDNS).
For example:
vpn.example.comThen your client configuration can use:
Endpoint = vpn.example.com:51820If your public IP changes, your DDNS service updates the hostname.
Step 11: Create the Client Configuration
Create a client configuration file:
nano client1.confUse:
[Interface]
PrivateKey = CLIENT1_PRIVATE_KEY
Address = 10.8.0.2/24
DNS = 1.1.1.1

[Peer]
PublicKey = SERVER_PUBLIC_KEY
Endpoint = YOUR_PUBLIC_IP_OR_DDNS:51820
AllowedIPs = 10.8.0.0/24, 192.168.1.0/24
PersistentKeepalive = 25
Replace:
CLIENT1_PRIVATE_KEYwith:
sudo cat /etc/wireguard/client1_private.keyReplace:
SERVER_PUBLIC_KEYwith:
sudo cat /etc/wireguard/server_public.keyAnd replace:
YOUR_PUBLIC_IP_OR_DDNSwith your public IP or DDNS hostname.
What Does AllowedIPs Do?
This is one of the most important WireGuard settings.
Our example:
AllowedIPs = 10.8.0.0/24, 192.168.1.0/24means that traffic destined for:
10.8.0.0/24or:
192.168.1.0/24goes through the VPN.
This is called a split-tunnel configuration.
It allows you to access your home network while normal Internet traffic continues to use the client’s regular Internet connection.
Full-Tunnel VPN Configuration
You can instead route all IPv4 Internet traffic through your home VPN.
Change:
AllowedIPs = 10.8.0.0/24, 192.168.1.0/24to:
AllowedIPs = 0.0.0.0/0You can include IPv6:
AllowedIPs = 0.0.0.0/0, ::/0Now the traffic flow becomes:
Laptop
   │
   │ WireGuard
   ▼
Raspberry Pi
   │
   ▼
Home Router
   │
   ▼
Internet
This makes the remote device appear to access the Internet through your home connection.
For a simple home-network VPN, however, split tunneling is often the better starting point.
Step 12: Start WireGuard
Start the VPN:
sudo wg-quick up wg0Check its status:
sudo wg showYou should see something similar to:
interface: wg0
  public key: ...
  listening port: 51820

peer: ...
  allowed ips: 10.8.0.2/32
Step 13: Start WireGuard Automatically
Enable the service at boot:
sudo systemctl enable wg-quick@wg0You can also start it through systemd:
sudo systemctl start wg-quick@wg0Check:
sudo systemctl status wg-quick@wg0Step 14: Install WireGuard on Your Client
Install the official WireGuard client on your device.
WireGuard provides clients for major desktop and mobile platforms. (WireGuard)
You can use:
- Windows
- macOS
- Linux
- Android
- iPhone/iPad
Step 15: Import the Client Configuration
You have several options.
Desktop
Import:
client1.confinto the WireGuard application.
Mobile
You can transfer the configuration to your phone or generate a QR code.
QR codes are particularly convenient for phones.
Step 16: Generate a QR Code
Install qrencode:
sudo apt install qrencode -yThen generate a QR code from the configuration:
qrencode -t ansiutf8 < client1.confThe terminal will display a QR code.
Open the WireGuard mobile application and choose:
Add a tunnel → Scan from QR code
Scan the displayed code.
Security warning
The QR code contains the client’s private key and VPN configuration.
Treat it as sensitive information.
Don’t post it publicly or send it to people you don’t trust.
Step 17: Activate the VPN
Activate the newly imported WireGuard tunnel.
The client should connect to:
YOUR_PUBLIC_IP_OR_DDNS:51820If everything is configured correctly, the client will establish a handshake with the Raspberry Pi.
Step 18: Check the WireGuard Handshake
On the Raspberry Pi:
sudo wg showLook for:
latest handshakeYou should see a recent timestamp.
You may also see:
transfer: 12.34 KiB received, 15.67 KiB sentThis confirms that encrypted traffic is flowing through the tunnel.
Step 19: Test the VPN
From the remote client, try:
ping 10.8.0.1You should receive a response from the WireGuard server.
Then try your Raspberry Pi’s LAN IP:
ping 192.168.1.50If your routing and firewall configuration are correct, the Raspberry Pi should respond.
Step 20: Access Your Home Network
Now try accessing another device on your LAN.
For example:
192.168.1.100You could potentially access:
http://192.168.1.100or:
\\192.168.1.100depending on the service.
This is where a Raspberry Pi WireGuard server becomes particularly useful.
Access CasaOS Remotely
If CasaOS is running on the Raspberry Pi, you can access:
http://192.168.1.50through the VPN.
Your traffic follows:
Remote Laptop
      │
  WireGuard
      │
      ▼
Raspberry Pi
      │
    CasaOS
No public CasaOS port needs to be exposed.
Access Jellyfin Remotely
If Jellyfin runs on:
192.168.1.50:8096you can use:
http://192.168.1.50:8096while connected to the VPN.
This is an excellent way to keep a personal Jellyfin server private.
Access Nextcloud Remotely
Similarly, if Nextcloud is running on your Raspberry Pi:
https://192.168.1.50or your internal hostname can be used through the VPN.
Nextcloud may require the VPN-accessible hostname or IP to be included in its trusted_domains configuration.
Use WireGuard with Pi-hole
WireGuard and Pi-hole make a particularly useful combination.
You can configure the client to use your Pi-hole as DNS.
For example:
[Interface]
PrivateKey = CLIENT1_PRIVATE_KEY
Address = 10.8.0.2/24
DNS = 192.168.1.50
Now DNS requests from the VPN client can go through Pi-hole.
The architecture becomes:
Remote Phone
     │
 WireGuard
     │
     ▼
Raspberry Pi
     │
   Pi-hole
     │
     ▼
   Internet
This can give you network-wide DNS filtering even when you’re away from home.
Full-Tunnel VPN with Pi-hole
If you want all traffic to go through your home connection, use:
AllowedIPs = 0.0.0.0/0and:
DNS = 192.168.1.50The result is:
Remote Device
      │
      │ WireGuard
      ▼
Raspberry Pi
      │
      ├── Pi-hole DNS
      │
      ▼
 Home Router
      │
      ▼
  Internet
This requires the Raspberry Pi’s NAT and forwarding configuration to be correct.
WireGuard Firewall Configuration
If you’re using a firewall such as UFW, allow the WireGuard UDP port:
sudo ufw allow 51820/udpThen check:
sudo ufw statusHowever, don’t blindly enable UFW on a remote Raspberry Pi without understanding its existing rules. You can accidentally lock yourself out of SSH.
WireGuard and nftables
Modern Raspberry Pi OS releases use the Linux networking stack with nftables underneath the system firewall tooling.
If you encounter NAT or forwarding problems, don’t assume that an older iptables-only tutorial will work exactly as written.
Check the current firewall configuration:
sudo nft list rulesetThe exact rules you need depend on your Raspberry Pi OS version, firewall configuration, and whether you’re using iptables compatibility tools.
Why VPN Clients Can’t Access the Internet
A common problem is:
“The VPN connects, but I can’t browse the Internet.”
This usually happens when:
- IP forwarding isn’t enabled.
- NAT isn’t configured.
- The wrong interface is specified.
- Firewall forwarding is blocked.
AllowedIPsis incorrect.
Check forwarding:
sysctl net.ipv4.ip_forwardYou want:
net.ipv4.ip_forward = 1Then check the default interface:
ip routeYou might see:
default via 192.168.1.1 dev eth0In that case, eth0 is the interface connected to your LAN/Internet.
Why the VPN Connects but LAN Devices Don’t Work
If the VPN handshake succeeds but you can’t access:
192.168.1.xcheck:
Client AllowedIPs
Make sure the client includes:
AllowedIPs = 10.8.0.0/24, 192.168.1.0/24IP forwarding
Check:
sysctl net.ipv4.ip_forwardFirewall
Make sure forwarding isn’t blocked.
Return routing
The LAN device needs a route back to the VPN network.
NAT on the Raspberry Pi can simplify this because the LAN devices see traffic as coming from the Raspberry Pi’s LAN address.
Why the Client Can’t Connect at All
If there is no handshake, check the following.
Port forwarding
Make sure:
UDP 51820is forwarded to the Raspberry Pi.
Public IP
Verify your endpoint is correct.
DDNS
If your public IP changes, confirm that your hostname points to the current address.
CGNAT
If your ISP uses CGNAT, traditional inbound WireGuard may not work.
Firewall
Make sure UDP 51820 isn’t being blocked.
How to Check the Listening Port
Run:
sudo ss -lunp | grep 51820You should see WireGuard listening on UDP port 51820.
Monitor WireGuard
The most useful command is:
sudo wg showIt provides:
- Interface
- Public key
- Listening port
- Peers
- Latest handshake
- Transfer statistics
- Allowed IPs
For troubleshooting, this should be one of your first commands.
Generate Additional Clients
You should create a unique key pair for every device.
For example:
Laptop
10.8.0.2

Phone
10.8.0.3

Tablet
10.8.0.4
Don’t reuse the same client private key across multiple devices.
Add a Second Client
Generate another key:
cd /etc/wireguard

sudo wg genkey | sudo tee phone_private.key
sudo cat phone_private.key | wg pubkey | sudo tee phone_public.key
Add another peer to:
/etc/wireguard/wg0.confFor example:
[Peer]
PublicKey = PHONE_PUBLIC_KEY
AllowedIPs = 10.8.0.3/32
Then restart WireGuard:
sudo systemctl restart wg-quick@wg0WireGuard Configuration Structure
The server configuration might eventually look like:
[Interface]
Address = 10.8.0.1/24
ListenPort = 51820
PrivateKey = SERVER_PRIVATE_KEY

PostUp = iptables -A FORWARD -i wg0 -j ACCEPT; iptables -A FORWARD -o wg0 -j ACCEPT; iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE
PostDown = iptables -D FORWARD -i wg0 -j ACCEPT; iptables -D FORWARD -o wg0 -j ACCEPT; iptables -t nat -D POSTROUTING -o eth0 -j MASQUERADE

[Peer]
PublicKey = LAPTOP_PUBLIC_KEY
AllowedIPs = 10.8.0.2/32

[Peer]
PublicKey = PHONE_PUBLIC_KEY
AllowedIPs = 10.8.0.3/32

[Peer]
PublicKey = TABLET_PUBLIC_KEY
AllowedIPs = 10.8.0.4/32
Each peer gets its own VPN address.
Use PersistentKeepalive for Mobile Devices
Mobile devices often move between networks and may sit behind NAT.
In the client configuration:
PersistentKeepalive = 25can help maintain connectivity through NAT devices.
This is especially useful for phones and laptops that frequently switch between Wi-Fi and cellular networks.
WireGuard Security Recommendations
A VPN server is still an Internet-facing service.
Follow these practices:
Keep Raspberry Pi OS updated
sudo apt update
sudo apt full-upgrade
Protect private keys
Never publish:
server_private.key
client_private.key
Use unique keys
Every device should have its own key pair.
Remove lost devices
If a phone or laptop is lost, remove its peer configuration from the server.
Don’t expose unnecessary ports
Ideally, your router only needs the WireGuard UDP port for remote VPN access.
Use strong SSH security
Don’t expose SSH unnecessarily if you don’t need public SSH access.
WireGuard vs Tailscale
If you’re deciding between WireGuard and Tailscale, both are excellent options, but they solve the problem differently.
| Feature | WireGuard | Tailscale |
|---|---|---|
| Open source protocol | Yes | Uses WireGuard |
| Manual configuration | Required | Minimal |
| Port forwarding | Usually required | Usually not |
| Public IP required | Usually | No for normal use |
| CGNAT friendly | Not directly | Yes |
| Device management | Manual | Excellent |
| Subnet routing | Yes | Yes |
| Raspberry Pi | Excellent | Excellent |
| Beginner friendly | Moderate | Excellent |
| Maximum control | Excellent | Very good |
Choose WireGuard if:
- You want complete control.
- You have a public IP.
- You can configure port forwarding.
- You want to learn VPN networking.
- You want a minimal VPN implementation.
Choose Tailscale if:
- Your ISP uses CGNAT.
- You don’t want to configure port forwarding.
- You have multiple devices.
- You want easy device management.
- You want a simpler setup.
For a beginner building a Raspberry Pi home server, Tailscale is usually easier. For someone who wants to learn and control the entire VPN infrastructure, WireGuard is an excellent choice.
WireGuard vs OpenVPN
WireGuard is generally simpler to configure than traditional OpenVPN deployments.
| Feature | WireGuard | OpenVPN |
|---|---|---|
| Configuration | Simple | More complex |
| Performance | Excellent | Good |
| Modern cryptography | Yes | Yes |
| Codebase | Small | Larger |
| Mobile support | Excellent | Excellent |
| Raspberry Pi | Excellent | Excellent |
| Ease of setup | ⭐⭐⭐⭐⭐ | ⭐⭐⭐ |
For a new Raspberry Pi VPN server, WireGuard is generally the more attractive option.
Should You Use PiVPN?
If you don’t want to manually create keys and configuration files, PiVPN is another option worth considering.
PiVPN provides an installer and management commands designed to simplify VPN deployment on Raspberry Pi and Debian-based systems.
For example, the Raspberry Pi documentation has demonstrated PiVPN with WireGuard using:
curl -L https://install.pivpn.io | bashand then creating VPN clients with:
pivpn addFor this article, however, we used a manual WireGuard installation because it gives you a better understanding of how the VPN works.
WireGuard with CasaOS
If your Raspberry Pi already runs CasaOS, WireGuard can provide remote access to your services.
For example:
                    Internet
                       │
                    WireGuard
                       │
                       ▼
                Raspberry Pi 5
                       │
                     CasaOS
                       │
         ┌─────────────┼─────────────┐
         │             │             │
      Jellyfin      Nextcloud     Pi-hole
This is a particularly strong home-server architecture.
You can keep your applications private while accessing them remotely through the VPN.
WireGuard with Jellyfin
For a private Jellyfin installation, WireGuard can be preferable to exposing Jellyfin directly to the Internet.
Instead of:
Internet
   │
Port 8096
   │
Jellyfin
use:
Phone
 │
WireGuard
 │
Raspberry Pi
 │
Jellyfin
This is particularly useful for personal and family media servers.
WireGuard with Nextcloud
The same approach works with Nextcloud.
Your remote laptop connects to your home VPN:
Laptop
   │
WireGuard
   │
Raspberry Pi
   │
Nextcloud
   │
SSD
You can then access Nextcloud using its private address without necessarily exposing the application publicly.
WireGuard as a Remote Home-Lab VPN
One of the best uses for a Raspberry Pi WireGuard server is remote administration.
Imagine you’re traveling and need access to:
- Proxmox
- NAS
- Raspberry Pi
- Home Assistant
- Router
- Switch
- Internal websites
Instead of exposing each service individually:
Internet
 │
 ├── NAS port
 ├── Home Assistant port
 ├── SSH port
 ├── Proxmox port
 └── Other ports
you can expose only:
Internet
   │
UDP 51820
   │
Raspberry Pi
   │
VPN
   │
Home LAN
This is much cleaner.
Backup Your WireGuard Configuration
Your WireGuard configuration contains important private keys.
Back up:
/etc/wireguard/but protect the backup carefully.
You don’t want your private keys stored in an unsecured public repository.
A backup should include:
wg0.conf- Server private key
- Client configurations
- Client keys
- Documentation of your network settings
What Happens If the Raspberry Pi Reboots?
If you’ve enabled:
sudo systemctl enable wg-quick@wg0WireGuard should start automatically when the system boots.
Check:
sudo systemctl status wg-quick@wg0This is important for a VPN server because you don’t want to manually start the service after every power outage.
Troubleshooting Checklist
If your WireGuard VPN isn’t working, go through this list.
Server
sudo wg showService
sudo systemctl status wg-quick@wg0Listening port
sudo ss -lunp | grep 51820IP forwarding
sysctl net.ipv4.ip_forwardRouting
ip routeNetwork interface
ip addrFirewall
sudo nft list rulesetRouter
Verify:
UDP 51820 → Raspberry PiClient
Check:
- Public endpoint
- Server public key
- Client private key
- AllowedIPs
- VPN address
- DNS
- PersistentKeepalive
Important: CGNAT Can Break This Setup
One of the most important limitations of hosting your own VPN at home is CGNAT.
If your ISP gives your router a private or shared WAN address and places your connection behind another layer of NAT, an incoming WireGuard connection may never reach your Raspberry Pi.
In that situation, you can consider:
Option 1: Tailscale
Easy and generally works without inbound port forwarding.
Option 2: Ask your ISP for a public IP
Some ISPs offer this as an option.
Option 3: Use a VPS
Deploy WireGuard on a VPS and establish a connection between your home network and the VPS.
This is more advanced but provides greater control.
Is a Raspberry Pi Good for a VPN Server?
Yes.
A Raspberry Pi is an excellent platform for a personal WireGuard server.
It’s particularly useful for:
- Remote home access
- Home labs
- Secure SSH access
- Accessing NAS devices
- Jellyfin
- Nextcloud
- Home Assistant
- Pi-hole
- Internal websites
The Raspberry Pi doesn’t need to be especially powerful for a normal VPN workload.
The more important factors are:
- Internet bandwidth
- Network configuration
- Router capabilities
- ISP limitations
- VPN routing
- Firewall configuration
Recommended Raspberry Pi VPN Setup
For a typical home server, I’d use:
                 Internet
                     │
               UDP 51820
                     │
                     ▼
                 Router
                     │
                     ▼
              Raspberry Pi 5
                     │
                 WireGuard
                     │
              10.8.0.0/24
                     │
        ┌────────────┼────────────┐
        │            │            │
      Laptop        Phone       Tablet
        │
        └──────── Home LAN ────────┐
                                   │
                         ┌─────────┼─────────┐
                         │         │         │
                       NAS     Home Assistant  PC
For the best experience, connect the Raspberry Pi to your router through Gigabit Ethernet.
Final Thoughts
A Raspberry Pi running WireGuard can provide a secure and inexpensive way to access your home network remotely.
The basic architecture is simple:
Remote Device
      │
      │ Encrypted WireGuard Tunnel
      ▼
  Home Router
      │
      ▼
 Raspberry Pi
      │
      ▼
  Home Network
The most important parts of the configuration are:
- Give the Raspberry Pi a stable LAN address.
- Install WireGuard.
- Enable IP forwarding.
- Generate unique keys.
- Configure
wg0.conf. - Forward UDP 51820 on your router.
- Configure your client.
- Test the WireGuard handshake.
- Configure routing and NAT.
- Secure your private keys.
If your ISP supports inbound connections, WireGuard is an excellent choice for a self-hosted Raspberry Pi VPN.
If your ISP uses CGNAT or you want a much simpler setup, consider Tailscale instead.
For the home-server ecosystem you’re building, a particularly useful combination is:
Raspberry Pi + CasaOS + WireGuard + Jellyfin + Nextcloud + Pi-hole
This gives you a low-power server that you can securely manage and access from almost anywhere.
Frequently Asked Questions
Can I use a Raspberry Pi as a VPN server?
Yes. Raspberry Pi OS supports WireGuard, making the Raspberry Pi a practical VPN server for personal and home-lab use. (WireGuard)
Is WireGuard free?
Yes. WireGuard is free and open-source software.
What port does WireGuard use?
The default WireGuard port is UDP 51820.
Do I need to forward port 51820?
For a conventional self-hosted WireGuard server behind a home router, yes, you normally need to forward the WireGuard UDP port to the Raspberry Pi.
Can I use WireGuard without port forwarding?
Not in the conventional direct-to-home-server setup. If you cannot accept inbound connections, Tailscale or another NAT-traversing solution may be a better choice.
Can I access my entire home network?
Yes. With appropriate routing and firewall configuration, the Raspberry Pi can provide VPN clients access to your LAN.
Can WireGuard route all Internet traffic through my home?
Yes. Configure the client with:
AllowedIPs = 0.0.0.0/0and configure forwarding/NAT correctly on the Raspberry Pi.
Is WireGuard better than Tailscale?
Neither is universally better. WireGuard gives you more direct control and a simpler underlying protocol, while Tailscale makes device management and NAT traversal much easier.
Can I run WireGuard and Tailscale on the same Raspberry Pi?
Yes, but you should understand the routing and firewall interactions before doing so. For a beginner, it’s usually simpler to choose one VPN solution for a particular purpose.
Recommended Links
- Install Tailscale on Raspberry Pi
- Install Pi-hole on Raspberry Pi
- Install Jellyfin on Raspberry Pi
- Install Nextcloud on Raspberry Pi
- Install CasaOS on Raspberry Pi
- CasaOS vs OpenMediaVault
- How to Build a Home Server with a Single Board Computer
- Best Single Board Computers for Home Servers
- Best SBC for Home Assistant